One every five minutes
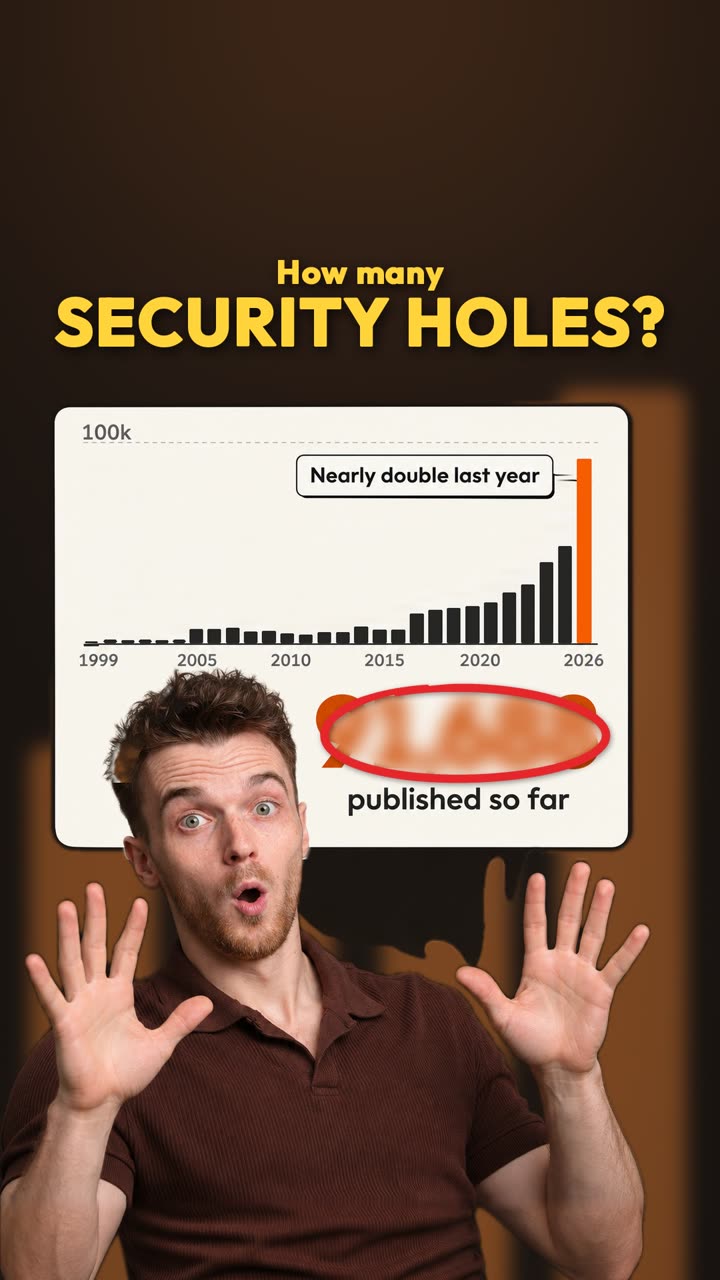
Every five minutes or so, a new security hole in software is made public. From 1 January to 12 November 2026, the US National Vulnerability Database (NVD) published 96,852 of them [1]. That’s one every 4.7 minutes, and in October alone it was about 550 a day.
When the short was made, the count stood at 91,688, up to 5 November [1]. That’s Bradley’s “over ninety-one thousand”. A week later it was past 96,000.
Each hole gets an ID called a CVE, short for Common Vulnerabilities and Exposures, and goes on a public list. Think of it as a recall notice, but for software: it names the product, the versions that are affected and what’s wrong, so it can be fixed. Our wiki shows how to read a CVE entry, part by part.
The catch is that attackers read the same list. It tells them exactly what’s broken, and in which versions.
The list is exploding
In the short, Bradley says this year is nearly double last year. That was true when he recorded it. By 12 November, 2026 had passed double the whole of 2025, with seven weeks still to go.
He puts the rise down to AI, which is now hunting for bugs too. The sources back AI as one driver, with some care needed. In June, FIRST, the global forum of incident response teams, raised its 2026 forecast to about 66,000 CVEs [6], and Help Net Security’s report on it puts the surge down mostly to AI tools finding flaws on their own. The real count has already blown past that forecast.
Google’s threat intelligence team found that monthly disclosures doubled between January and August 2026 [4]. It also warns that automatic ID assignment in open-source projects inflates the raw counts: Linux kernel bugs alone produced about 5,000 CVEs in those months, and none was seen exploited as a zero-day, a hole attacked before anyone knew about it.
Attackers are using more of them, though. Google counted 141 newly disclosed holes exploited in the wild from January to August 2026, already more than the 127 in all of 2025. On AI’s part in the attacks themselves, it is more careful, calling attacks on AI-found flaws “an early indicator rather than an established trend”.
The ones attackers use
Only a small share of CVEs are ever used in an attack. For this year’s disclosures up to August, Google’s figure works out at about one in 431. CISA, the US government’s cyber defence agency, keeps a separate list of the ones with reliable evidence of attacks: the Known Exploited Vulnerabilities catalog, or KEV. On 10 November 2026 it held 1,779 entries [3].
Microsoft is miles ahead, and Windows on its own has more entries than any other company. For a worked example of one hole on the list, our wiki breaks down PHP2Shell, whose first bug CISA added on 26 October 2026.
Holes like these are now the number one way into a breach. In Verizon’s 2026 Data Breach Investigations Report, exploiting a security hole overtook stolen passwords as the most common first step, for the first time in the report’s 19 years.
Faster than the fix
Attackers move fast. Google Mandiant tracks how long, on average, they take to use a new hole, counted from when the fix comes out.
- 2018 to 201963 days after the fix
- 2020 to early 202144 days after the fix
- 2021 to 202232 days after the fix
- 20235 days after the fix
- M-Trends 2026, from 2025 investigationsAbout 7 days before the fix existed
A negative number means attackers were in before there was a fix to install. Mandiant’s M-Trends 2026 puts the average at about minus 7 days [13], which means exploitation now routinely starts before a patch is even released.
The fix is boring, but it works. Update your stuff as soon as a fix comes out. Turn on automatic updates, so the fix arrives without you having to remember, and stop tapping “Remind me later”.
On an iPhone or iPad, it’s Settings, General, Software Update, Automatic Updates. Apple’s guide says Automatically Install puts updates on overnight while the phone is charging and on Wi-Fi. For Windows, our Windows settings write-up starts with Windows Update.
Update your stuff today
- iPhone or iPad: Settings › General › Software Update › Automatic Updates, and turn on Automatically Install.
- Windows: Settings › Windows Update › Check for updates, and restart if it asks.
- Android: search Settings for “update” and install anything waiting.
- Browser and apps: if one shows an update or restart button, use it. That’s a fix waiting to go on.
- Next time anything offers an update, choose install, not “Remind me later”.
What this doesn’t prove
Written from the public sources listed below. Counts re-checked 13 Nov 2026 against NVD, CVE.org and CISA.
- CVE counts change every day. The 2026 figures are NVD’s, for CVEs published 1 January to 12 November 2026 with rejected records left out, checked on 13 November 2026. Earlier years are CVE.org’s.
- A CVE count measures holes reported, not danger. Some projects give every bug an ID automatically, which inflates the totals, and only a small share is ever used in attacks.
- The CISA list only includes holes with reliable evidence of attacks, so it is a floor, not a full count.
- Verizon’s figures come from the breaches in its report, not every breach. Each edition covers roughly the year before it.
- The AI link is partly unproven. Google calls attacks on AI-found flaws an early indicator, and FIRST’s AI-driven forecast has already been overtaken by the real count.
Go deeper on our wiki
Sources
- CVE API 2.0: CVEs by published date, rejected records excludedNIST National Vulnerability Database, counted 13 Nov 2026
- CVE Program metrics: published CVE records by yearCVE.org, read 13 Nov 2026
- Known Exploited Vulnerabilities catalog, version 2026.11.10CISA, 10 Nov 2026
- Vulnerability Discovery and Exploitation Trends in the AI EraGoogle Threat Intelligence Group, 30 Sep 2026
- Google finds vulnerability disclosures doubled as AI changes which flaws get discoveredSiliconANGLE, 30 Sep 2026
- AI vulnerability discovery is pushing 2026 CVEs toward 66,000Help Net Security, 15 Jun 2026
- 2026 Verizon DBIR: The New Era of Cyber ThreatseSecurity Planet, 21 May 2026
- Key findings from the Verizon DBIR 2026Tenable, 19 May 2026
- Verizon DBIR: Vulnerability exploitation is the dominant initial access vectorHelp Net Security, 20 May 2026
- 2025 Data Breach Investigations ReportVerizon, 23 Apr 2025
- 2024 Data Breach Investigations ReportVerizon, 1 May 2024
- How Low Can You Go? An Analysis of 2023 Time-to-Exploit TrendsGoogle Cloud, Mandiant, 15 Oct 2024
- M-Trends 2026: Data, Insights, and Strategies From the FrontlinesGoogle Cloud, Mandiant, 23 Mar 2026
- Update your iPhone or iPadApple Support (UK), read 13 Nov 2026