Policy & Governance
Policies are useful when people can follow them and named owners can enforce them. We review the current set, find what is missing and write the documents with your legal and leadership teams.
Who this is for
Organisations with missing policies, outdated templates or an audit requirement that the current documents do not meet.
- You have been asked for a policy that does not exist yet.
- Your existing documents no longer match the systems and practices in use.
- You have an audit or certification coming that the current set will not pass.
How the engagement runs
Read the current documents
Check which policies exist, when they were last reviewed and whether they match current practice.
Confirm the requirements
Map the required policies to your regulatory duties, customer commitments and chosen frameworks.
Draft around real practice
Write the controls, responsibilities and exceptions around the way your people and systems work.
Work through the wording
Review the drafts with leadership, legal and the teams responsible for applying the controls.
Set ownership and review dates
Record who owns each policy, how it will be introduced and when it should be reviewed again.
Why we work this way
A generic template rarely survives contact with the business
People ignore a rule that conflicts with their normal work. The wording needs to reflect actual systems and responsibilities.
A policy should help someone decide
Clear boundaries and named escalation routes matter when a decision has to be made quickly.
Missing topics surface at awkward times
AI use, data classification and incident responsibilities are easier to settle before an audit or incident forces the discussion.
What you receive
A set of policies ready for internal approval, a record of the gaps found and a practical guide for introducing and maintaining the new documents.
- Review of the current policy set and a documented gap analysis
- Policy drafting aligned with your sector and regulatory duties
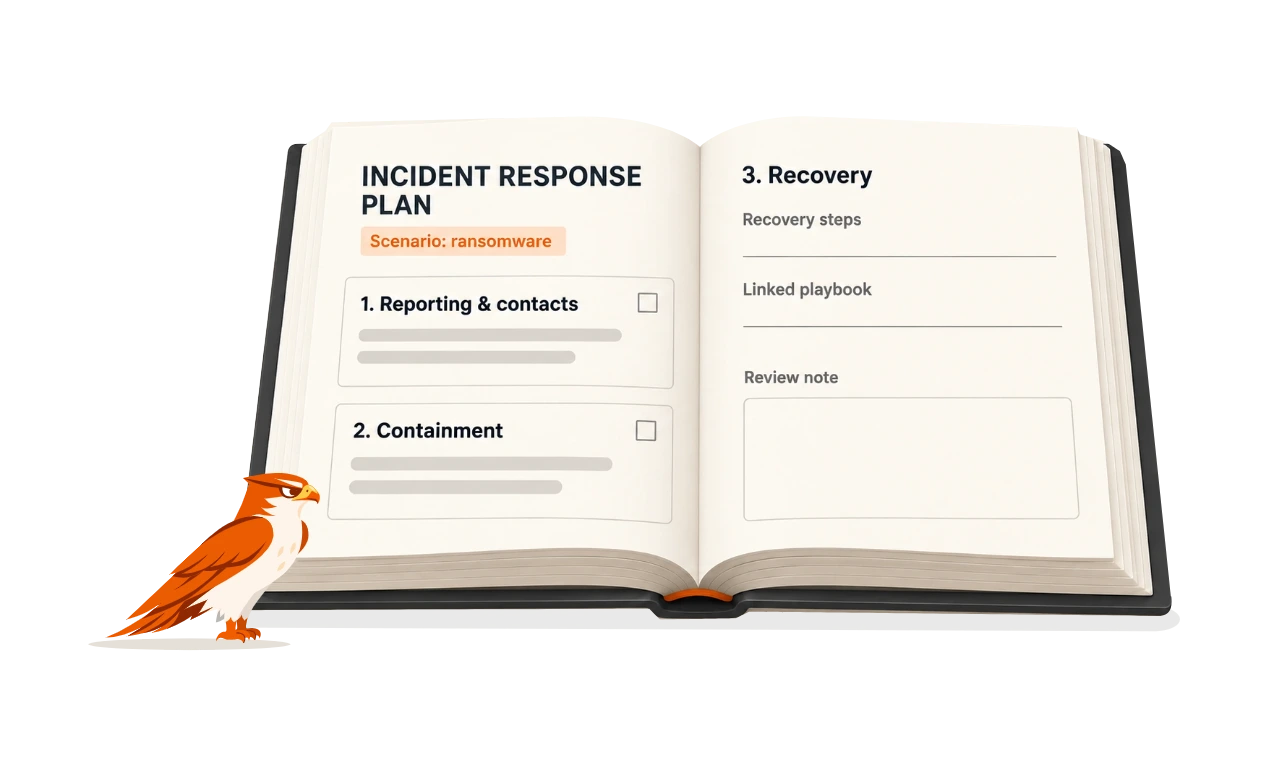
- Coverage for AI use, acceptable use, incident response and other agreed topics
- Review sessions with leadership and legal teams
- Guidance for ownership, rollout and future review
Sample report, fictional client
Why choose us for this work
Experience across several sectors
We have written policy sets for healthcare, finance and technology organisations with different regulatory duties.
Security and compliance considered together
The documents address audit requirements while remaining workable for the teams expected to follow them.
Controls linked to your systems
Where possible, each requirement is tied to a technical control, an owner or a repeatable process.