Known malicious open source packages have passed 1.2 million
1.23 millionUp 75% year on year
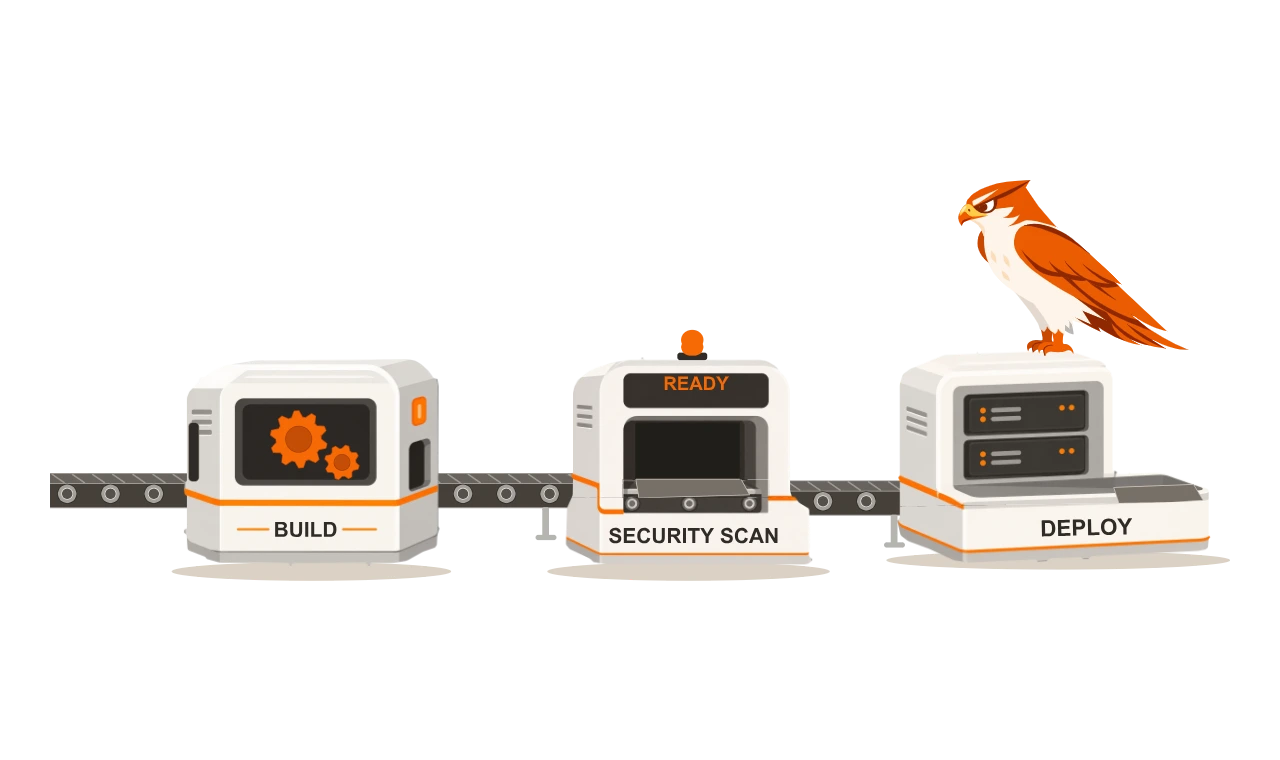
known malicious packages across npm, PyPI, Maven Central, NuGet and Hugging Face, after 454,600 new ones were found in 2025 alone. The report names developer machines and CI/CD pipelines as the execution environment those packages are built to reach.
704kOct 2024
829kApr 2025
1.23mJan 2026
This is why the review checks what runs during install and build, not only what ships to production.