
Detection engineering
SOC Use Case Review
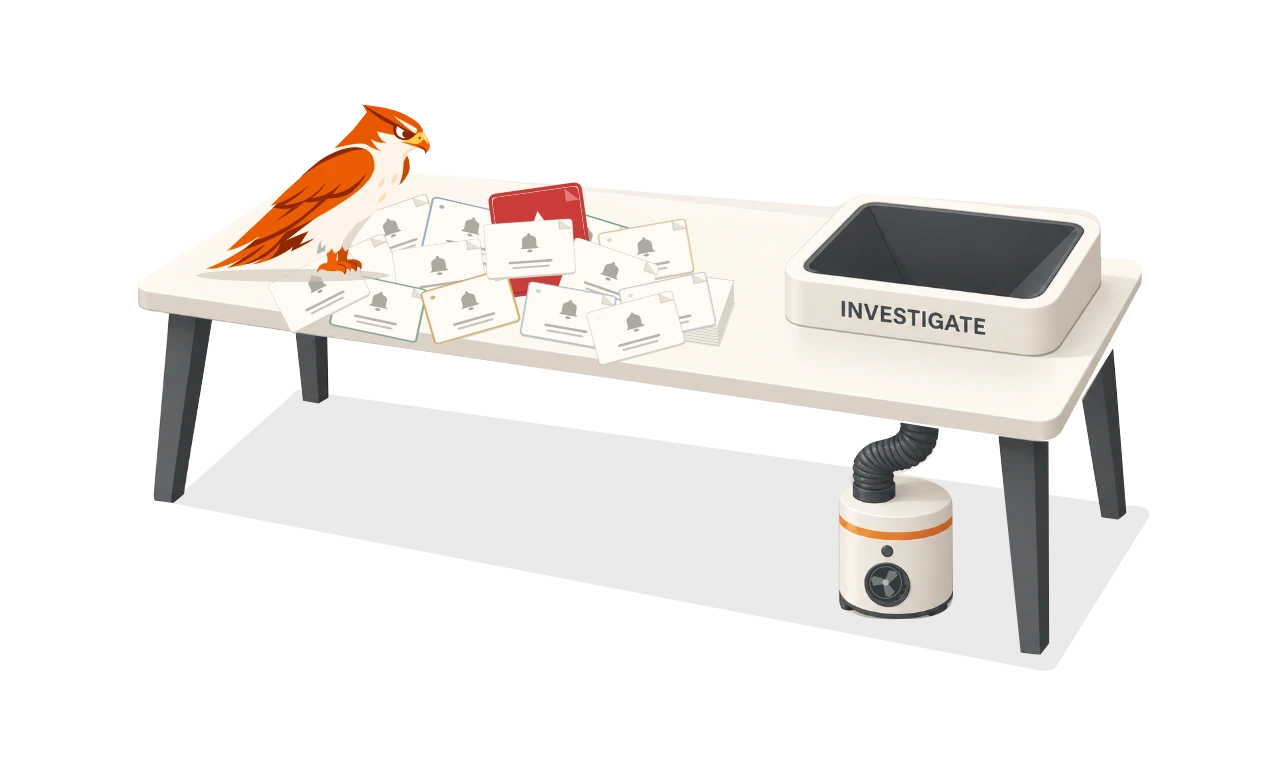
We inspect your SIEM detection rules, compare them with the systems your organisation relies on and identify alerts that are wasting analyst time.
What's included
- Review of active detection use cases and alert rules
- Mapping of critical systems to current monitoring coverage
- Checks for missing or poorly parsed log sources
- New use case proposals for unmonitored attack paths
- Prioritised recommendations for rule tuning and logging changes
- Tuned queries with exclusions specific to your environment, such as scanner ranges and known service accounts
What you receive
A detection health report that lists the tuning changes, proposed use cases and logging work in priority order, with a coverage matrix for your critical systems and each tuned query carrying the exclusions specific to your environment.